Posts

BUILDING OF ZERO TRUST MODEL ARCHITECTURE

Image
  Zero Trust Model is the new buzz of the cybersecurity system. With its modern approach for providing safe network coverage, it has become the first to go choice of users nowadays. With more cases being reported of breaching happening more from internal factors, the Zero Trust Model was developed. This security system works on the principle of  “trust, but verify” which means and apply as the way, your network system would trust and believe every user coming across but the access to the data and information is given once the user is providing the server with proper authentication and after they overcome the verification process. The working mechanism of the Zero Trust Model aims to safeguard data and access grants across the network by verifying the user identity and location. This security system works, inspects, and keeps track of everything, henceforth providing the network system with secured network parameters after analyzing the whole server usage and working process. B...

RECOMMENDATION FOR USING SSH KEYS

Image
SSH keys also commonly known as Secure Shell Protocol keys are the set of keys that allow the users to exchange data and files between two channels through a secure medium. The primary function of these key sets is to provide a secure private transaction medium to the users from both client end as well as server end. These keys are mostly used for the Git repository function.   Public key cryptography is mostly used by SSH keys for communicating. Asymmetric algorithms are used in public-key cryptography. While using SSH keys, the key used to encrypt the message is totally contrary to the one used to decrypt it.   These keys actually comprise two sets namely - Public key and private key. A public key is held by all, which means anyone can get access to it without much trouble, though the access to the private key is only with the users and the permission to step into the data is only granted after proper authentication is provided with proper passwords and valid I’d ...

RBAC (Role-Based Access Control ) and its Alternatives

Image
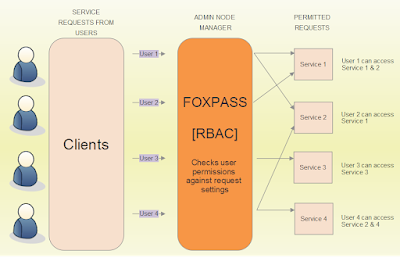
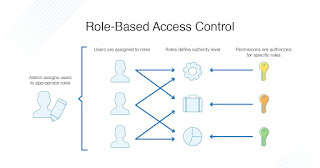
  Role-based access control is the security network system that allows the grant data access to the person on the basis of their role at a specific platform. It actually means the grant access to particular information will be given to an individual as per their job profile and only that much detail would be provided to them as they need to perform their tasks. Implementing RBAC for security, allows the higher authorities to build a tight network system for the users which henceforth makes access management easier. By following the concept of a Role-based access control system, the participant gets only limited access to the firm's data. This security level makes sure no other person intrudes on the specifics for no use and without any purpose. There are a lot of ways by which one can perform functions to follow RBAC by the use of the custom level privilege. The custom level privilege is actually the user level mode, which somehow means that privilege to the facts and figures wou...

A - Z Guide For SSH Keys (Understanding SSH Keys)

Image
  SSH keys are actually the set of keys used to safeguard the network from intruders. SSH stands for Secure Socket Shell, in a simple language it is also known as Secure Shell. These pairs of keys work on the SSH protocol. SSH protocol was developed after a scenario of trespassing was observed on a network system. SSH Protocol was developed in 1995 by Tatu Ylonen. The main idea behind introducing the SSH Protocol was to protect the servers from attackers who try to make an attempt to gain access to your network with the help of usernames and passwords. And so just to make sure that no one steps in your network area without proper authentication SSH keys are developed. The main function of these keys is to provide users with secure private network transactions from both ends, whether being client-side or server-side. SSH keys  are mostly used for allowing single sign-in only at one time. These pairs of keys are used for managing networks, operating systems, and configurations.S...

SERVER TESTING AND MONITORING TOOLS - FreeRADIUS

Image
  FreeRADIUS is one of the most used and developed RADIUS servers in the world. This network system was formed in the year 1999 by Miquel van Smoorenburg and Alan DeKok. The FreeRADIUS network is responsible for providing internet services and network authentication to almost one-third of internet users all over the world.  Over 100 million people use FreeRADIUS on a daily basis to access the internet. It is actually a project which works and aims to provide more authentication ways and types than any other open-source server. The freeRADIUS project focuses on providing its users with : New Models Development. Submission of New Models. Patch Issues. FreeRADIUS, being the network provider for the majority of the population, becomes somewhat necessary to keep a check on its functioning and to keep a track of its server testing and monitoring tools. These tools are used to keep a track of the system in use and to keep a check on the server’s performance as well. Server testing ...

CYBER SECURITY’S LATEST BUZZ - ZERO TRUST

Image
Zero trust is a cybersecurity hack, which is there to safeguard your online system. It says that brands or companies should not grant access to their online networks to anyone, be it, insider or outsider, without authentication. It simply says, that one should not grant access to your systems until you know who the user is and whether they are authorized or not.   The Zero Trust model was created by JOHN KINDERVAG, in the year 2010. His main idea behind introducing zero trust was to protect the company’s network within their own users, as there have been cases reported where the activities of cybercrime have taken place within the authorized networks. So, to make sure, no such activity happens within the organization user group, zero trust was developed. This security system works on the principle of, ‘never trust, always verify’ and also it follows the idea of ‘least-privilege’ access, which states that users will get only limited access to the data. Zero Trust works on the...

SECURITY SYSTEM WITH ACCESS CONTROL - RBAC

Image
  One can define role-based access control, as the method or network security system where the user is granted access to the data on the basis of the role they have at the organization they are working at. Basically, it means one can use the data of their firm, only on the basis of their job profile at the office. RBAC, is considered one of the best network security systems for business purposes, and almost every firm uses it. The grant access granted to a particular person at the institute varies on their position and the kind of data and information, they need to perform their tasks. Just in case, if few of the employees are working on more than one project, so they’d be getting access to the data and network systems, of all the live projects they are working on and once their work is done or finished, one can remove them from the grant access list of that particular data.   It is a security system, which works on the principle of restricting system access. It specifica...