Posts

LDAP User: What is it and what is it used for?
Image
There are terms that by their initials sound totally unknown. Such is the case of LDAP . Do you know its meaning and what LDAP users mean? How many times have we come across this name without knowing that it is well known in the computing area and that they refer to the Lightweight Directory Access Protocol?  It is, then, an important model that precisely allows the user to log into network computers, especially within organizations, whose characteristic is very similar to Windows Active Directory, an access manager for business users. LDAP user: What is this protocol and what is it used for? The LDAP user is the acronym for the Lightweight Directory Access Protocol, its name derives just a ceremonial formality in terms of applications through which users enjoy a service organized directory, hierarchical and distributed in search of diverse data in a corporate network environment. Hence its relationship with another manager, such as Windows Active Directory, which also manages us...
Secure Management of Privileged Access and Limit The Risk of Breaches

Image
Traditional peripheral computer security measures - such as software firewalls, DRM, complex password policies, and frequent spins - have proven to have their limits. If an unauthorized user obtains account information and login details, they can easily bypass these traditional systems. Recently, several large-scale cyber attacks have been attributed to unauthorized users taking advantage of privileged user access codes to gain access to an account and then to a network. Cyber ​​security professionals face a major problem. They must take steps to protect users and manage risk without limiting the productivity and satisfaction of their customers. With Foxpass, security professionals can control and monitor privileged access management while giving their privileged users the freedom to perform their duties. As part of its privileged access systems, Foxpass organizes security around the four “A”: Architecture, Authentication, Controlled Access, and Audit. Architecture: a discrete deploym...

Multiple authentications from SSH keys

Image
When you start to have a lot of servers to administer, SSH keys multiply. Indeed even if, as a general rule, the same key is used to authenticate on different machines, it is sometimes necessary to use other keys. Either connect with a different user account on the same device physically because we use several types of keys or because we want to avoid a single key allowing access to several machines. You will tell me that you can choose which key to use using ssh -i option, that's true, but like any good developer I'm a bit lazy, and if the machine can do it at my place, why bother me? It is, therefore possible, to use the file, ~/.ssh/config to indicate to the SSH Keys client which key it should use to connect and to which machine. This way our SSH client will always use the key attached to a particular host. The directive allows you to specify an alternative name, it also accepts an IP. It is quite possible to specify multiple hostnames for the "Host" directive; th...

802.1x Wi-fi Authentication Networks: The Benefits

Image
As more and more devices join public WiFi networks, concerns about user authentication and security continue to dominate the conversation. This is especially true when discussing the proper security protocols for large-scale guest WiFi networks that load hundreds, thousands, or even millions of users a day. Without the necessary security measures, users of the shared network are left vulnerable. Those who operate the network may also find the network unmanageable. As a basic security standard, high traffic public WiFi must be configured with enterprise WPA protocols that use an 802.1X authentication mechanism. 802.1x Wi-fi Authentication works in conjunction with two secure network protocols: Extensible Authentication Protocol over LANs (EAPoL) and Remote Authentication Dial-Up User Service (RADIUS) server. This makes 802.1x inherently more secure than its WPA-PSK or WPA2-PSK standards that require a shared password for all users to access the network. When to consider 802.1x Wi-fi Au...

Configure Role Based Access Control

Image
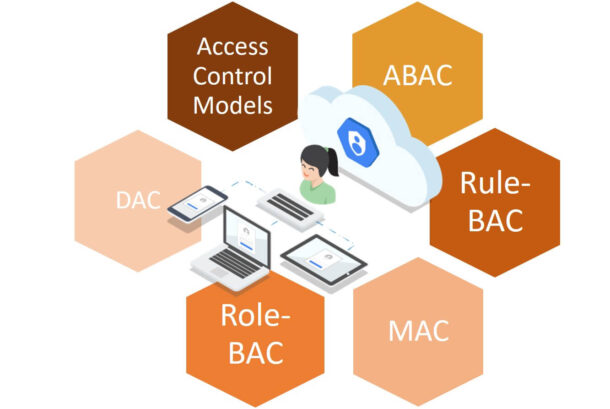
Foxpass provides role based access control  (RBAC), which allows you to grant access permissions based on the roles of individual users within your organization. In Foxpass, all users are added to Foxpass Cloud. As the first user in your organization, you must first create an account in Foxpass Cloud and then log in to the Foxpass Cloud credentials. You have the super administrator role, and by default, you have full access permissions in Foxpass. Later, you can create other users in your organization in Foxpass Cloud. Users who are created later and who log in to Foxpass as regular users are called delegated administrators. These users, by default, have all permissions except user administration permissions. However, you can grant specific user administration permissions to these delegated admin users. You can do this by creating appropriate policies and assigning them to these delegated users. User administration permissions can be found in Account > User administration. For m...

What is OpenRoaming Current?

Image
OpenRoaming Current is an open system that can connect your mobile device with a trusted and secured Wifi without any password or verification. This system allows you to use a secured wifi system without any credential login. We can say that OpenRoaming is an evolution of Pass point which is used to build dynamic and scalable relationships between service providers and wireless access networks. OpenRoaming currently has flexible policies which allow the service providers to find and figure the quality of the Wi-Fi networks their users attach to. Because all the Wi-Fi connections will be secured with enterprise-grade security protocols, the service providers can be at ease by knowing that their users are protected from Wi-Fi attacks. OpenRoaming tends to play a starring role in the future networking system, where convergence between Wi-Fi and cellular drives low connections in dense environments. OpenRoaming can be used as a synonymous network with free-for-all access.  Many compan...

LDAP - Benefits and Drawbacks

Image
Lightweight Directory Access Protocol ( LDAP ) is a security system that protects your data by ensuring that the information collected from other servers is safe through emailing.    In simple language, one can also define LDAP as a communication medium of Active Directory and other directory services.  Just like any other security system, LDAP also has its own set of benefits and drawbacks. Let’s have a look at them.   LDAP is security software that permits the users and applications to access, verify and find every sort of information required in an organization.    LDAP's main aim is to connect the organization users with clients, which makes it safe to share the data from both the server and client end to use and access.    LDAP is a vendor-neutral application protocol that functions to maintain the info in a directory in an organized way, which means it allows you to keep a guide and store information about its items. BENEFITS  ...